
TAIYO YUDEN Group Information Security Policy
Based on its mission and management philosophy, TAIYO YUDEN Group appropriately manages information assets entrusted by its customers and business partners and information assets held by TAIYO YUDEN Group, recognizes that the maintenance and improvement of information security is one of its major business challenges, has established the following policy and will continue to take measures for information security.
- 1. Compliance
- TAIYO YUDEN Group shall comply with laws, regulations, contractual requirements and other rules in respective countries and regions.
- 2. Improvement of management quality for business growth
- TAIYO YUDEN Group shall enhance its information security in order to improve its management quality for business growth and increase its social value as a corporation.
- 3.Appropriate management of information assets
- TAIYO YUDEN Group shall appropriately manage important information assets containing personal information, customer information, and trade secret information in order to protect the rights and interests of all stakeholders.
- 4. Response to information security incidents
- In the event of a security problem with information assets, TAIYO YUDEN Group shall promptly conduct an investigation into the cause of the problem, minimize the damage and endeavor to prevent recurrence in order to secure business continuity.
- 5. Continuous improvement of information security
- TAIYO YUDEN Group shall continuously endeavor to improve its information security through the establishment of a management system, as well as goal setting for resolution of information security issues, implementation of various measures, verification of their effectiveness, and carrying out of improvement activities.
Established on July 1, 2023
Officer in charge of Information Security
Basic Policy
TAIYO YUDEN positions information security as one of the most important management issues affecting business continuity and related to maintaining and enhancing corporate value over the medium- to long-term. We established a global information security management system and promote company-wide initiatives under the Information Security Policy.
At TAIYO YUDEN, we recognize various information assets, such as manufacturing processes, technical information, and customer information, as critical assets that are a source of competitive advantage, and we protect and manage these assets appropriately based on the level of risk.
Cyber risks, especially those affecting production sites, directly impact product quality and supply stability, thus we implement multi-layered security measures in the OT domain*, including production equipment, to strengthen the resilience of our manufacturing infrastructure.
-
*Note: Operational Technology. Hardware and software used to monitor and control equipment and production processes in plants and other facilities.
Governance Structure
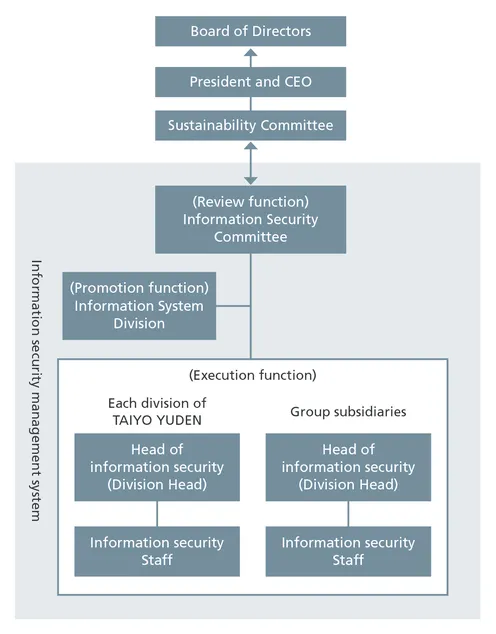
The Chief Information Security Officer (CISO) is responsible for overseeing company-wide information security measures and incident responses.
The Information Security Committee, chaired by the CISO, meets regularly to discuss the information security policy, the progress of various countermeasures, and the status of incident responses, among other matters. The details of these discussions and other key issues are reported to the Sustainability Committee twice a year and incorporated into management decision-making and oversight.
In practice, the Information System Division serves as the secretariat and promotes information security management across the Group.
Response when incidents occur
The Computer Security Incident Response Team (CSIRT) leads the initial response, ascertains the scope of impact, and implements containment and corrective measures. Incidents are promptly reported to the CISO, and when necessary, discussed by the Information Security Committee before being reported to the Sustainability Committee. As a result, we have established a system that ensures consistent decision-making and instruction, from on-site responses to management level resolutions.
Risk Management
We continuously assess risks related to information assets and implement a multi-layered management approach combining organizational, human, physical, and technical countermeasures.
In addition to establishing Group-wide regulations related to information security, we are working to improve information security literacy through training for new hires, regular training for all employees, role-based training, and suspicious email and incident response training.
In addition to controlling access to server rooms, production processes, and other critical areas, we implement integrated security measures combining a defense-in-depth, including malware countermeasures, vulnerability countermeasures, and network security measures, with access rights management and encryption.
Information Security Certification
TAIYO YUDEN Group is steadily advancing its efforts to obtain ISO 27001 and TISAX certifications to ensure high-level information security that meets our customers' trust.
ISO 27001 Certification Status
For details on the scope of each certification, please refer to the following certifications (PDF).
As of July 2026
| Sites | Registration Standard | Certification Authority | Certificate Number | Expiration Date | Certification |
|---|---|---|---|---|---|
| TAIYO YUDEN CO., LTD. Head Office/Takasaki Global Center/Sendai Sales Office/Gunma Sales Office/Nagoya Sales Office/Osaka Sales Office/Fukuoka Sales Office |
ISO/IEC 27001:2022 +Amd 1:2024 |
Bureau Veritas | JP024295 | Dec. 19, 2026 | |
| TAIYO YUDEN (U.S.A.) INC. | ISO/IEC 27001:2022 | Bureau Veritas | US021564 | Jun. 10, 2028 | |
| KOREA TAIYO YUDEN CO., LTD. | ISO/IEC 27001:2022 | Bureau Veritas | KR005009 | Dec. 29, 2028 | |
| TAIYO YUDEN (SINGAPORE) PTE. LTD. | ISO/IEC 27001:2022 | Bureau Veritas | SG005449 | Feb. 1, 2029 | |
| TAIYO YUDEN (MALAYSIA) SDN. BHD. | ISO/IEC 27001:2022 | Bureau Veritas | SG005449 | Feb. 1, 2029 | |
| TAIYO YUDEN TRADING (THAILAND) CO., LTD. | ISO/IEC 27001:2022 | Bureau Veritas | SG005449 | Feb. 1, 2029 | |
| TAIYO YUDEN EUROPE GmbH | ISO/IEC 27001:2022 | Bureau Veritas | DE016169 | Mar. 12, 2029 |
TISAX Certification Status
Several sites within the TAIYO YUDEN Group have obtained TISAX (Trusted Information Security Assessment Exchange) certification, as defined by the German Association of the Automotive Industry.
TISAX is a registered trademark and is governed by the ENX Association *1.
TISAX assessment results can be accessed via the ENX Portal *2. Please note that only individuals with an ENX Portal account are able to log in, and that TISAX and its results are not intended for public disclosure.
-
*1
-
*2
As of March 2026
| Sites | Assessment Level | Audit Provider | Scope-ID | Assessment-ID | Expiration Date |
|---|---|---|---|---|---|
| TAIYO YUDEN CO., LTD. Head Office | AL2 | Ernst & Young | SF78Y6 | AYTAI1-1 | Feb. 3, 2029 |
| TAIYO YUDEN CO., LTD. Tamamura Plant | AL2 | Ernst & Young | SRF971 | AYTAI2-1 | Feb. 3, 2029 |