
太阳诱电集团信息安全方针
基于本公司的使命和经营理念,妥善地管理客户和业务合作伙伴提供的信息资产和本公司持有的信息资产,并致力于维持和提高信息安全水平,太阳诱电集团(以下称为“本公司”)将其视为重要的经营课题之一,制定以下方针,采取持续性的信息安全措施。
- 1. 遵守法令
- 遵守各个国家和地区的法令、法规、合同要求以及其他规范。
- 2. 提高支撑事业发展的经营质量
- 通过强化信息安全,提高支撑事业发展的经营质量,提升企业的社会价值。
- 3.妥善管理信息资产
- 妥善管理包括个人信息、客户信息和营业机密信息的重要信息资产,保护所有利益相关者的权利和利益。
- 4. 针对信息安全事故的应对
- 当发生信息资产方面的安全问题时,迅速查明其原因,将其损失降至最低,并努力防止再次发生,确保事业的可持续性。
- 5. 持续改善信息安全
- 通过建立管理体系,设定有助于解决信息安全相关课题的目标、实施各种措施、确认有效性、开展改善活动,致力于持续改善信息安全。
2023年7月1日 制定
信息安全负责董事
Basic Policy
TAIYO YUDEN positions information security as one of the most important management issues affecting business continuity and related to maintaining and enhancing corporate value over the medium- to long-term. We established a global information security management system and promote company-wide initiatives under the Information Security Policy.
At TAIYO YUDEN, we recognize various information assets, such as manufacturing processes, technical information, and customer information, as critical assets that are a source of competitive advantage, and we protect and manage these assets appropriately based on the level of risk.
Cyber risks, especially those affecting production sites, directly impact product quality and supply stability, thus we implement multi-layered security measures in the OT domain*, including production equipment, to strengthen the resilience of our manufacturing infrastructure.
-
*Note: Operational Technology. Hardware and software used to monitor and control equipment and production processes in plants and other facilities.
Governance Structure
The Chief Information Security Officer (CISO) is responsible for overseeing company-wide information security measures and incident responses.
The Information Security Committee, chaired by the CISO, meets regularly to discuss the information security policy, the progress of various countermeasures, and the status of incident responses, among other matters. The details of these discussions and other key issues are reported to the Sustainability Committee twice a year and incorporated into management decision-making and oversight.
In practice, the Information System Division serves as the secretariat and promotes information security management across the Group.
Response when incidents occur
The Computer Security Incident Response Team (CSIRT) leads the initial response, ascertains the scope of impact, and implements containment and corrective measures. Incidents are promptly reported to the CISO, and when necessary, discussed by the Information Security Committee before being reported to the Sustainability Committee. As a result, we have established a system that ensures consistent decision-making and instruction, from on-site responses to management level resolutions.
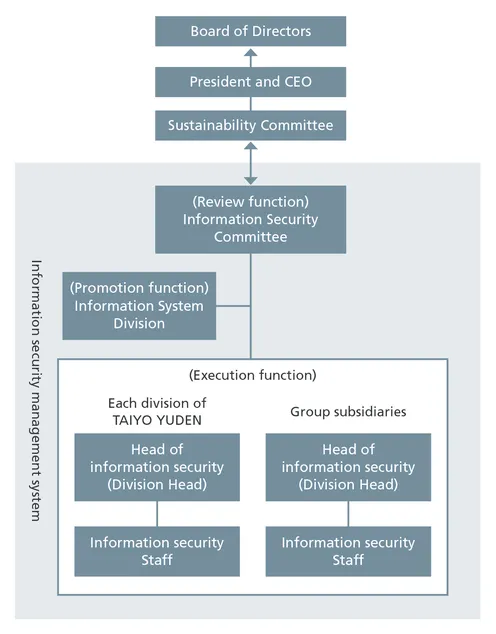
Risk Management
We continuously assess risks related to information assets and implement a multi-layered management approach combining organizational, human, physical, and technical countermeasures.
In addition to establishing Group-wide regulations related to information security, we are working to improve information security literacy through training for new hires, regular training for all employees, role-based training, and suspicious email and incident response training.
In addition to controlling access to server rooms, production processes, and other critical areas, we implement integrated security measures combining a defense-in-depth, including malware countermeasures, vulnerability countermeasures, and network security measures, with access rights management and encryption.
Information Security Certification
TAIYO YUDEN Group is steadily advancing its efforts to obtain ISO 27001 and TISAX certifications to ensure high-level information security that meets our customers' trust.
ISO 27001 Certification Status
For details on the scope of each certification, please refer to the following certifications (PDF).
As of July 2026
| Sites | Registration Standard | Certification Authority | Certificate Number | Expiration Date | Certification |
|---|---|---|---|---|---|
| TAIYO YUDEN CO., LTD. Head Office/Takasaki Global Center/Sendai Sales Office/Gunma Sales Office/Nagoya Sales Office/Osaka Sales Office/Fukuoka Sales Office |
ISO/IEC 27001:2022 +Amd 1:2024 |
Bureau Veritas | JP024295 | Dec. 19, 2026 | |
| TAIYO YUDEN (U.S.A.) INC. | ISO/IEC 27001:2022 | Bureau Veritas | US021564 | Jun. 10, 2028 | |
| KOREA TAIYO YUDEN CO., LTD. | ISO/IEC 27001:2022 | Bureau Veritas | KR005009 | Dec. 29, 2028 | |
| TAIYO YUDEN (SINGAPORE) PTE. LTD. | ISO/IEC 27001:2022 | Bureau Veritas | SG005449 | Feb. 1, 2029 | |
| TAIYO YUDEN (MALAYSIA) SDN. BHD. | ISO/IEC 27001:2022 | Bureau Veritas | SG005449 | Feb. 1, 2029 | |
| TAIYO YUDEN TRADING (THAILAND) CO., LTD. | ISO/IEC 27001:2022 | Bureau Veritas | SG005449 | Feb. 1, 2029 | |
| TAIYO YUDEN EUROPE GmbH | ISO/IEC 27001:2022 | Bureau Veritas | DE016169 | Mar. 12, 2029 |
TISAX Certification Status
Several sites within the TAIYO YUDEN Group have obtained TISAX (Trusted Information Security Assessment Exchange) certification, as defined by the German Association of the Automotive Industry.
TISAX is a registered trademark and is governed by the ENX Association *1.
TISAX assessment results can be accessed via the ENX Portal *2. Please note that only individuals with an ENX Portal account are able to log in, and that TISAX and its results are not intended for public disclosure.
-
*1
-
*2
As of March 2026
| Sites | Assessment Level | Audit Provider | Scope-ID | Assessment-ID | Expiration Date |
|---|---|---|---|---|---|
| TAIYO YUDEN CO., LTD. Head Office | AL2 | Ernst & Young | SF78Y6 | AYTAI1-1 | Feb. 3, 2029 |
| TAIYO YUDEN CO., LTD. Tamamura Plant | AL2 | Ernst & Young | SRF971 | AYTAI2-1 | Feb. 3, 2029 |
Our Initiatives
Our Group implements information security measures from organizational, human, physical, and technical perspectives.
- Organizational and Human Measures
- Our Group has established Group regulations related to information security and aims to improve information security literacy through internal education.
We conduct education at the time of joining the company, regular education for all employees, role-specific education, and training for responding to suspicious emails and incidents. - Physical Measures
- Our Group designates areas that require high confidentiality, such as server rooms and production processes, and implements heightened security levels and entry/exit management.
- Technical Measures
- Our Group implements multi-layered defense against cyber attacks, including malware countermeasures, vulnerability countermeasures, and network security countermeasures, as well as confidential information protection measures through access rights management and encryption.